Application security · Penetration testing

Muhammad Faqih

I test web, API and mobile applications and help developers fix security issues.

I have 3+ years of application security experience across web, API and mobile testing. I’ve worked on DAST in banking, validated findings manually, and written reports that help developers reproduce and fix issues.

OSCP+ / OSCPeWPTXeMAPTPT1

Portfolio

Selected work

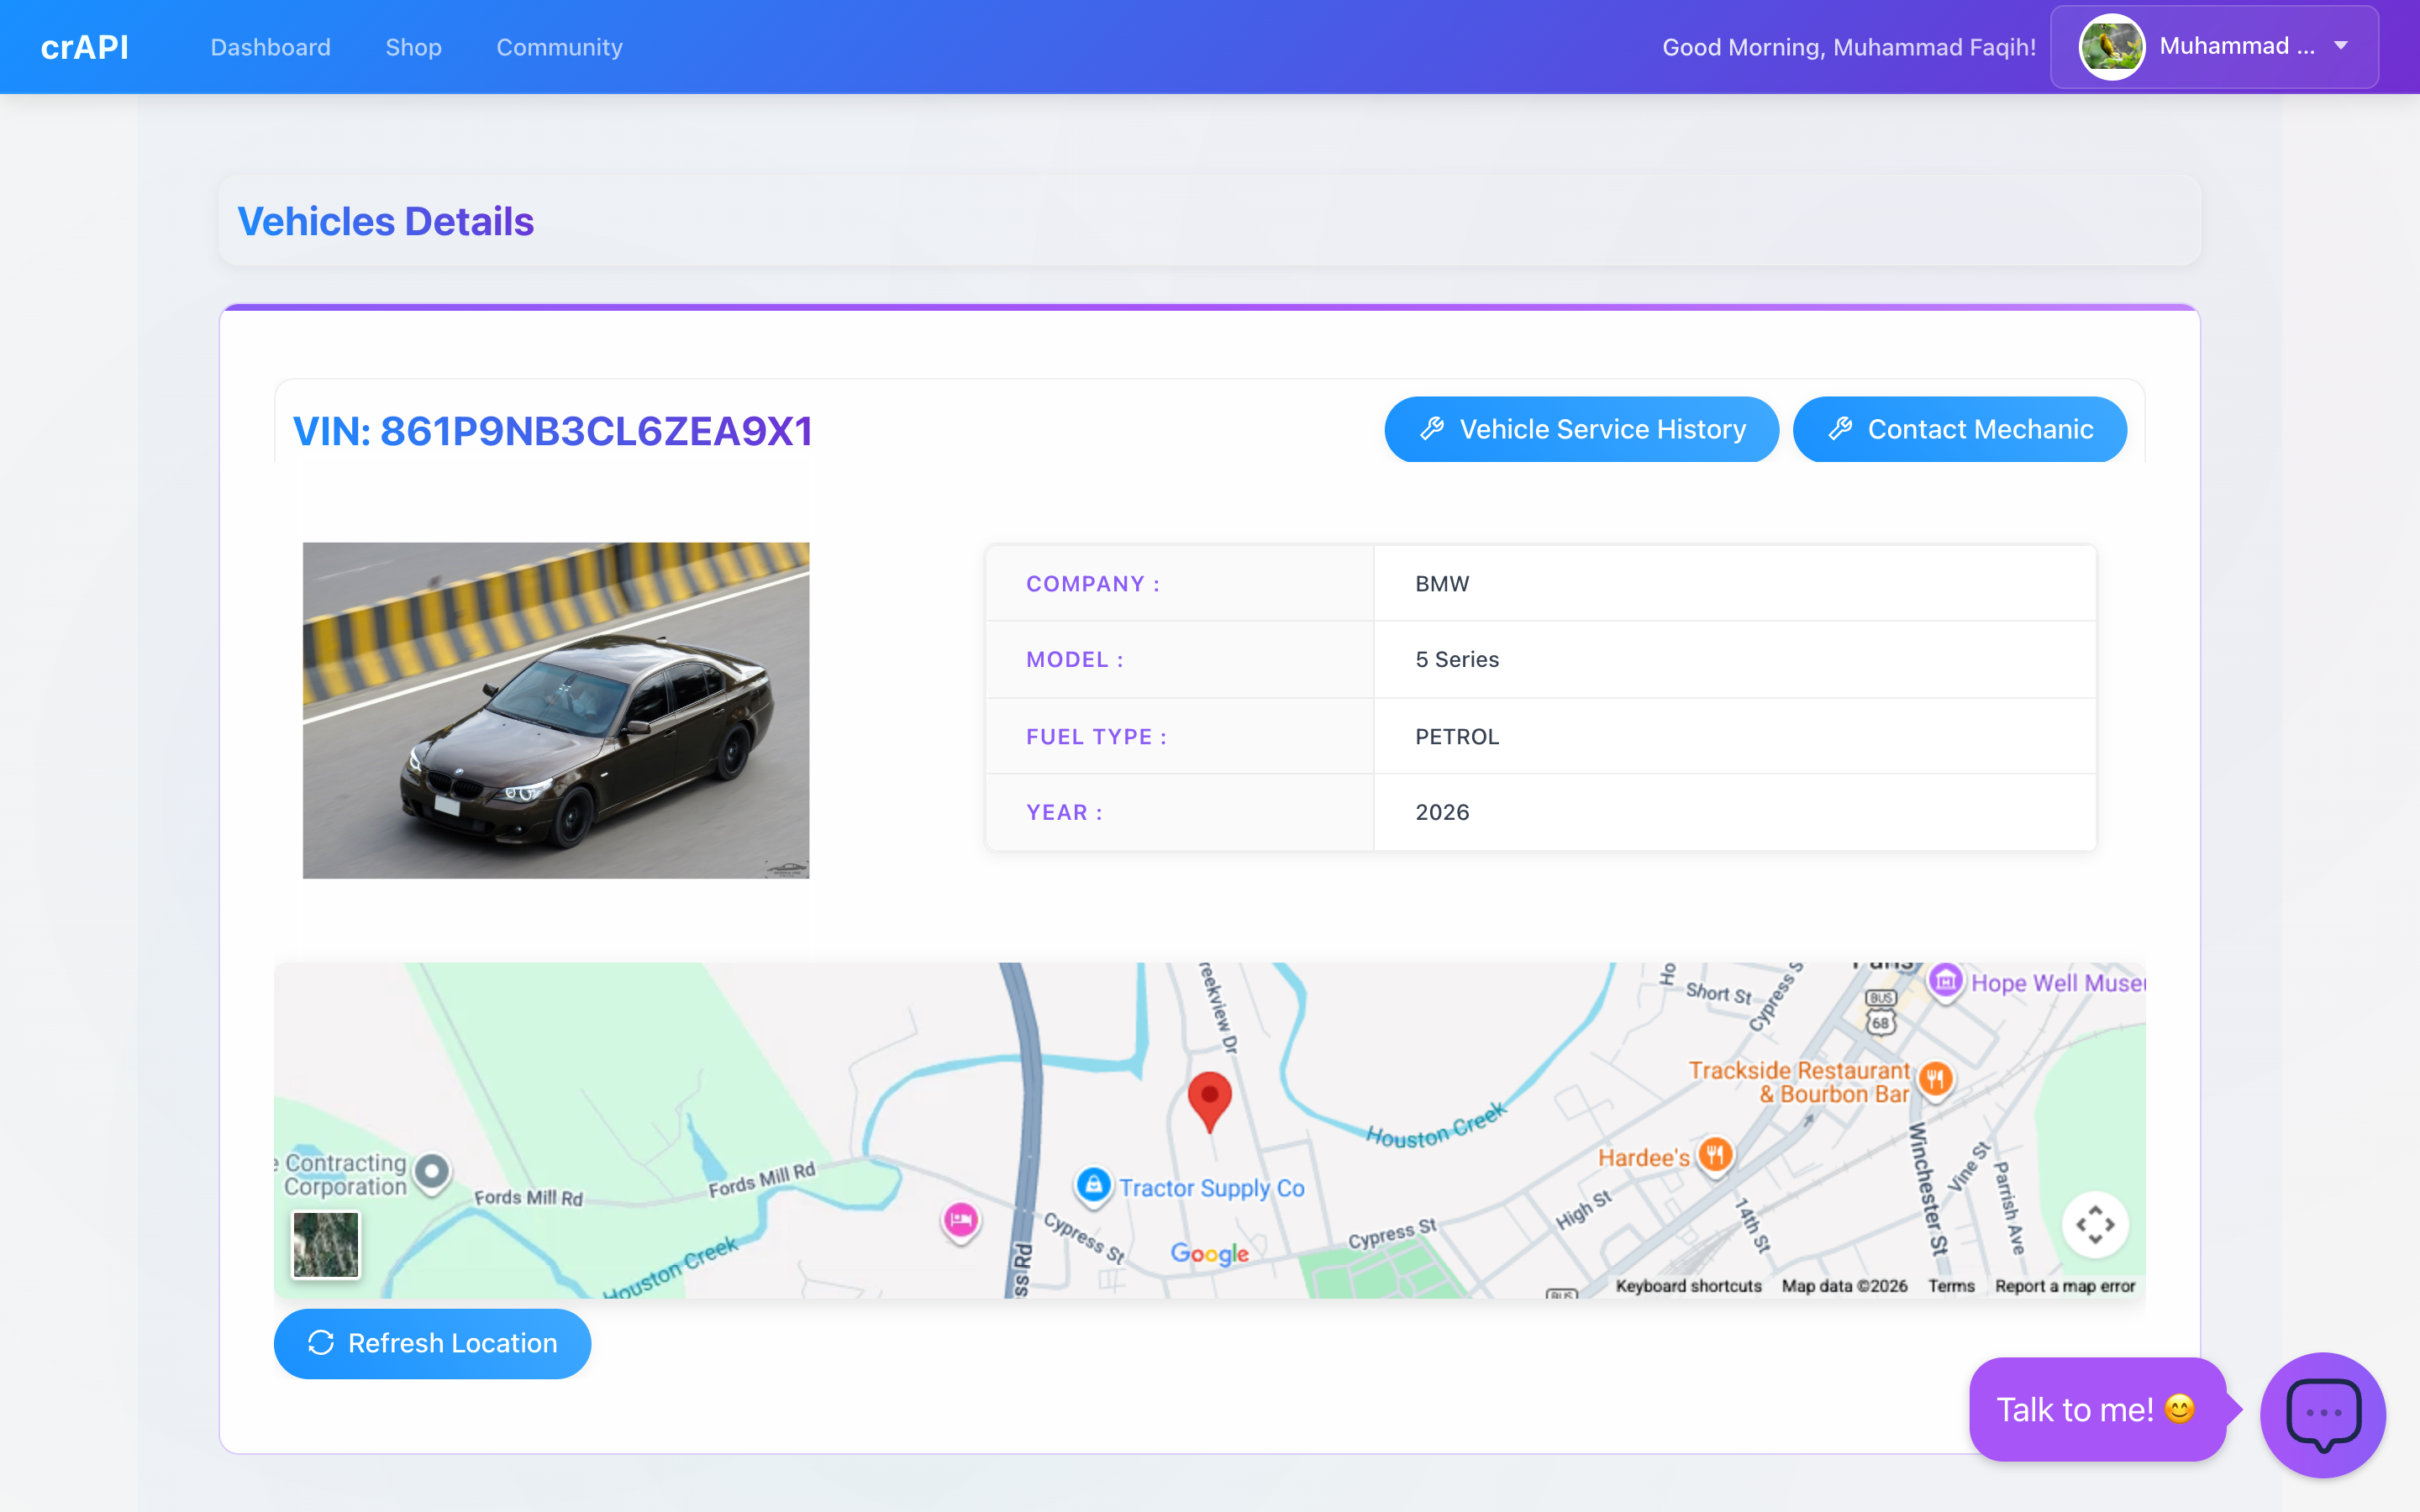
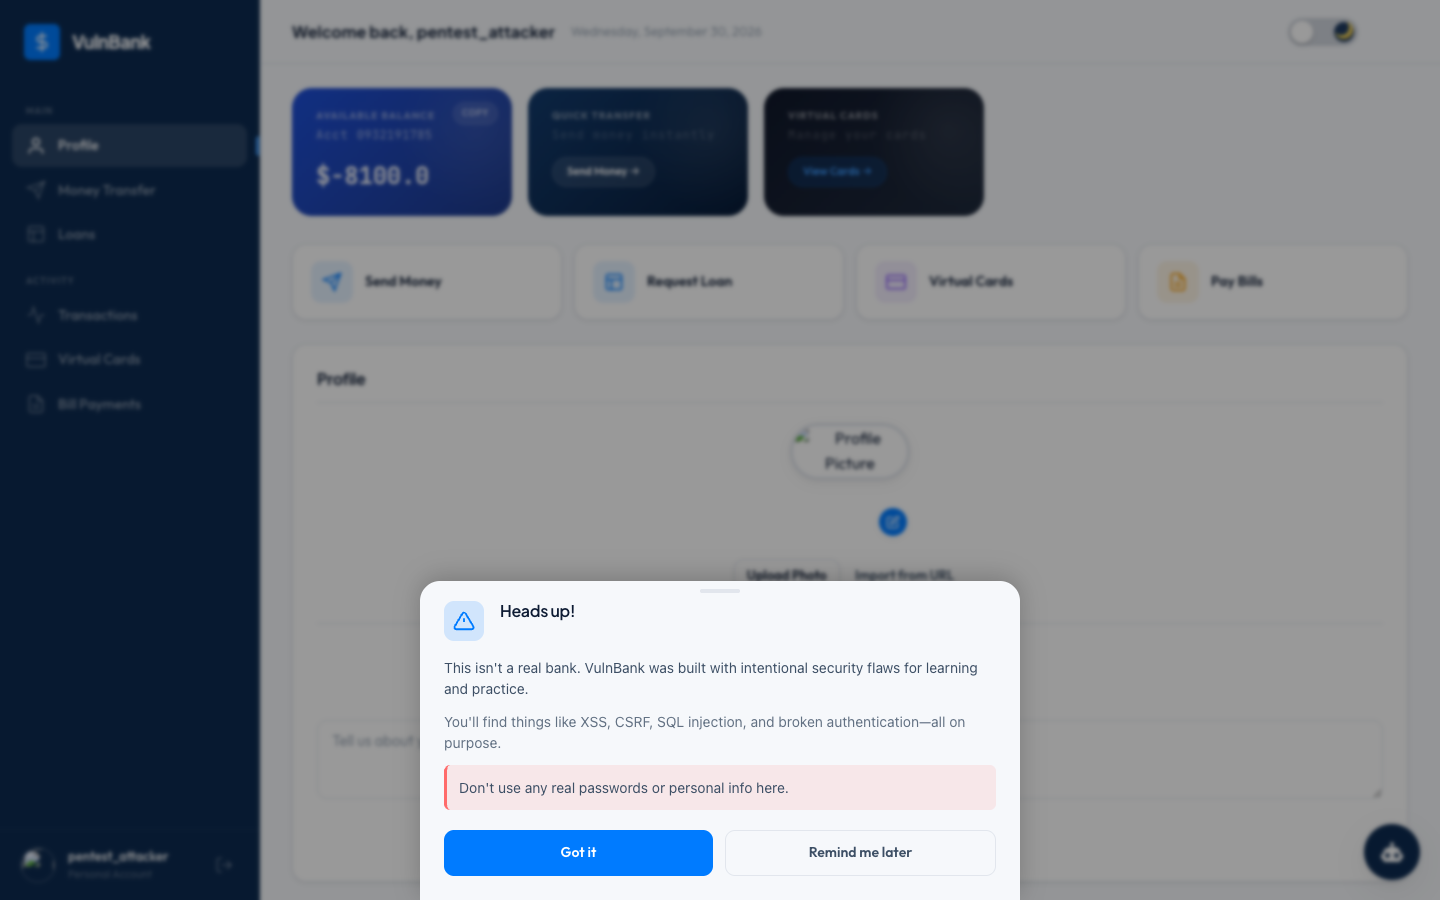
Two lab assessments and an open-source tool: what I tested, how I approached it, and what you can review.

03Open-source tool

Burp-TCP

Rust + Java

How do I inspect desktop traffic outside an HTTP proxy?

Approach
I routed TCP connections through a Rust SOCKS5 relay, with controls provided by a Java extension in Burp Suite.
Result
Inspect captured bytes, pause traffic in either direction, and resend data from Burp Suite. Source code and automated tests are available on GitHub.

Architecture

  1. Desktop application
  2. Rust SOCKS5 relay
  3. TCP target

Java Burp extension · WebSocket + Protobuf

What an assessment includes

A clear scope, findings your team can verify, and practical advice on what to fix.

01

Scope and coverage

The applications, features and boundaries covered, with any testing limitations made clear.

02

Steps to reproduce

Requests, responses, screenshots and notes that help another engineer verify the issue.

03

Findings and fixes

An explanation of the issue, its impact and affected behavior, followed by practical recommendations.

Contact

Have a role or assessment in mind?

Tell me about the role, or the application and scope you need tested.

faqih@siberfaqih.com

If we connected on Upwork, please keep pre-contract discussions there.